Exploit and payload research
Connect delivery to behavior.
Study the exploits and payloads used in targeted spyware, including threats such as Pegasus. Connect delivery to processing and execution.
- Input
- Behavior
- Execution
BELDRIN is a research phone running full iOS emulation, with physical iPhone behavior and working Apple services. It supports the discreet investigation of targeted digital threats in sensitive environments, so security teams can examine covert activity, establish the facts and inform a measured response.
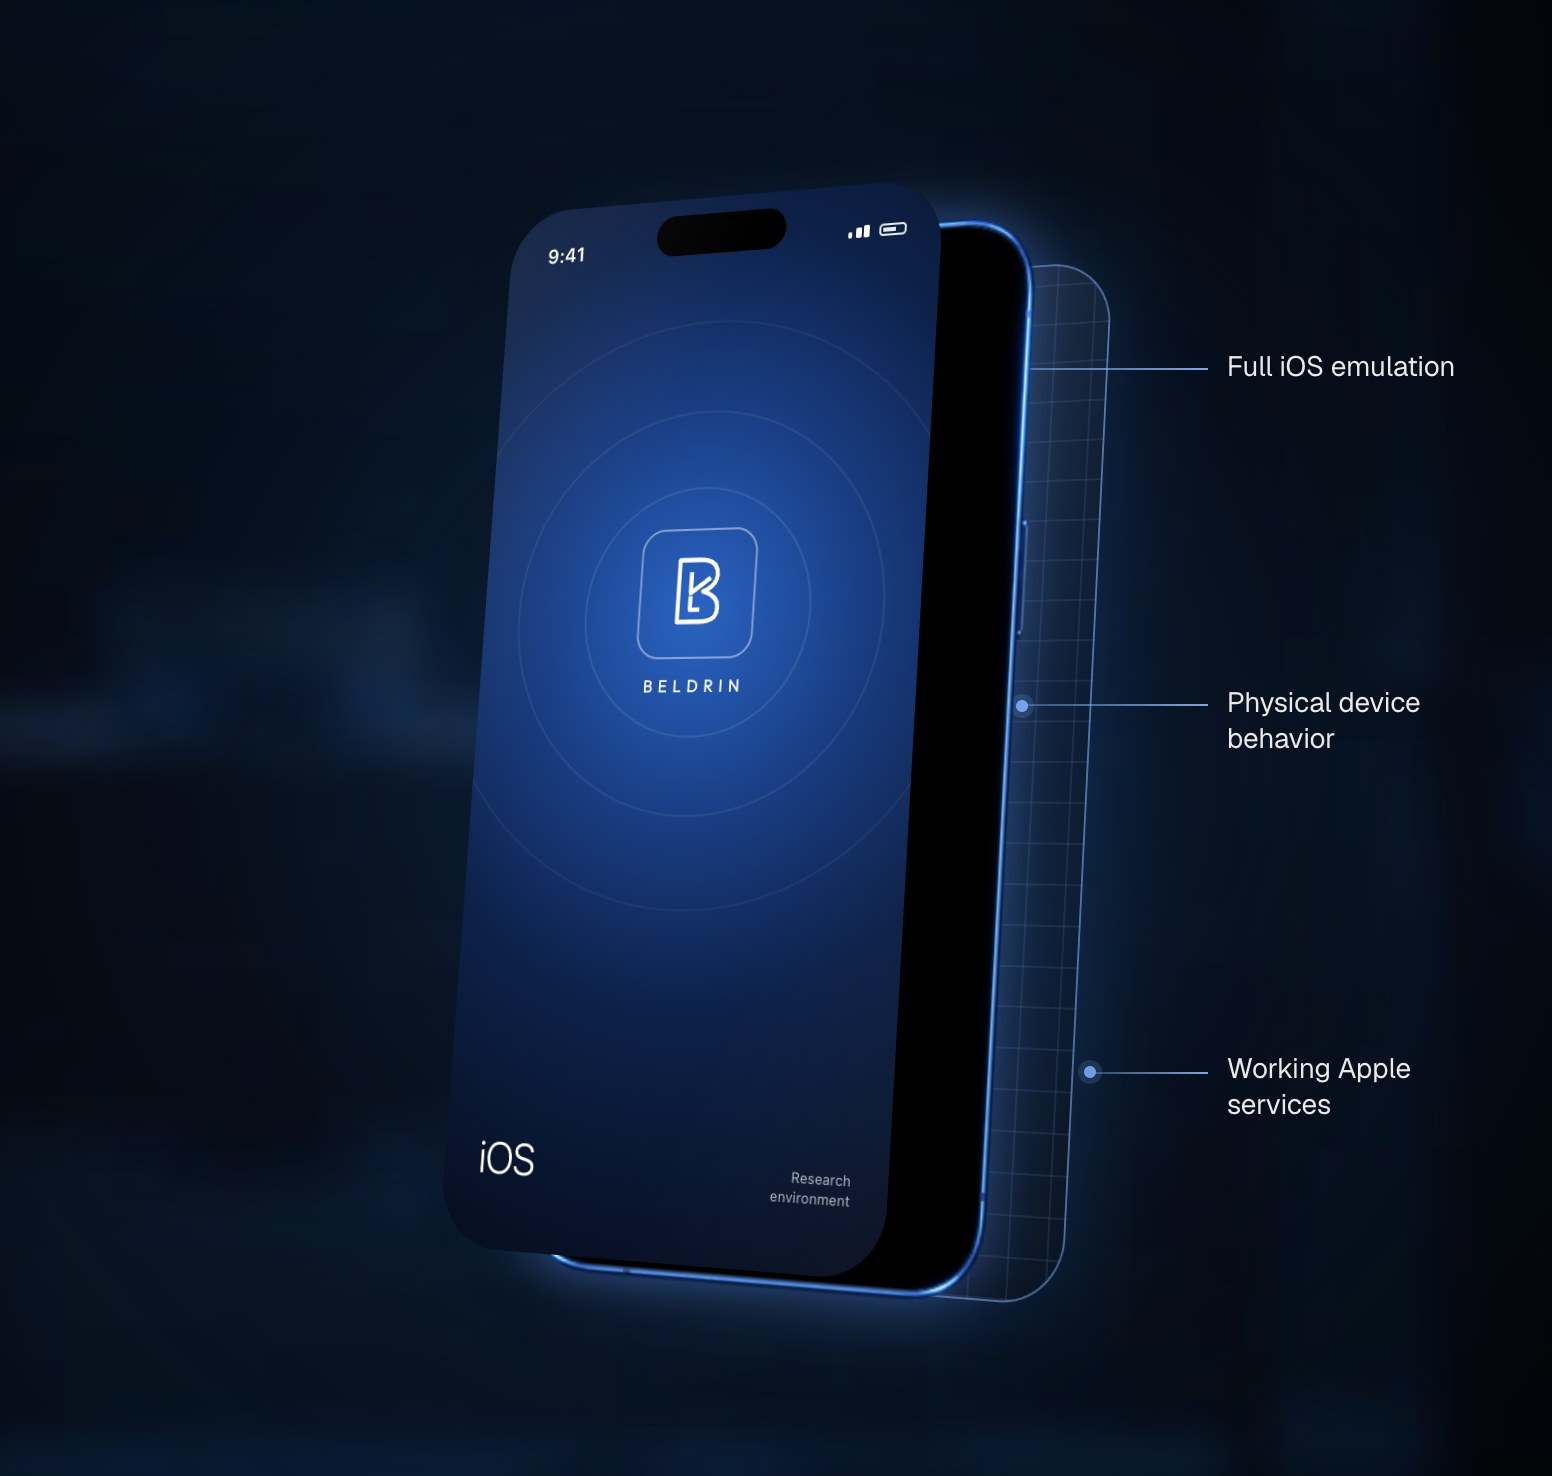
Physical iPhone behavior and working Apple services create a connected environment for capturing covert attacks. Preserve the exploit and examine its execution inside the device.
Device behavior supports payload capture and investigation. Conceptual research device illustration.
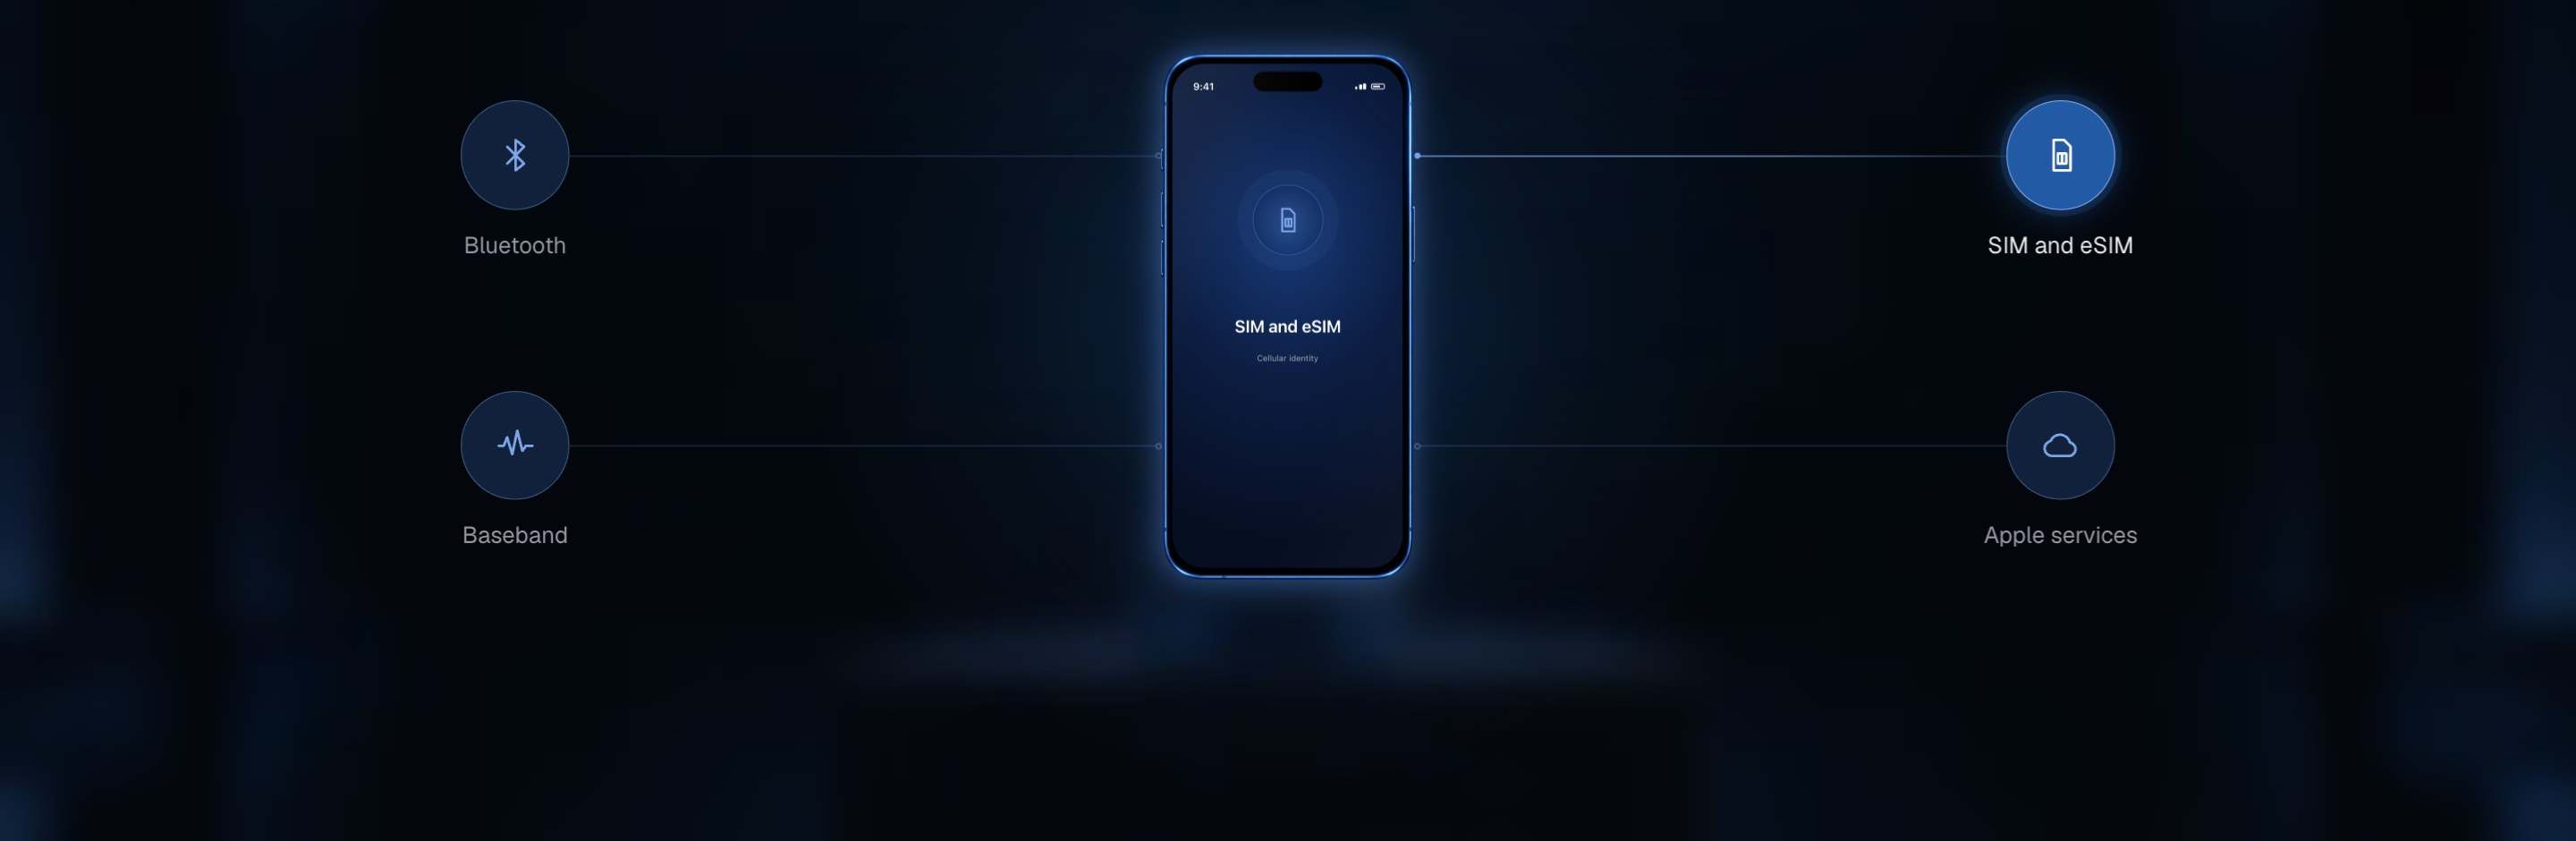
Bluetooth, physical SIM and eSIM, baseband and Apple services stay within reach of the investigation, because an attack may use any of them.
Proximity activity. Bluetooth support brings a proximity-based attack surface into the research environment, so activity from nearby devices can be studied.
Cellular identity. Physical SIM and eSIM support give the research phone a cellular identity for connected investigations.
Cellular functionality. Baseband support brings cellular functionality into the environment used to capture and investigate attacks.
Connected to the ecosystem. Working Apple services keep the research phone connected to the ecosystem targeted payloads may use.
Select a connection to explore the research phone.
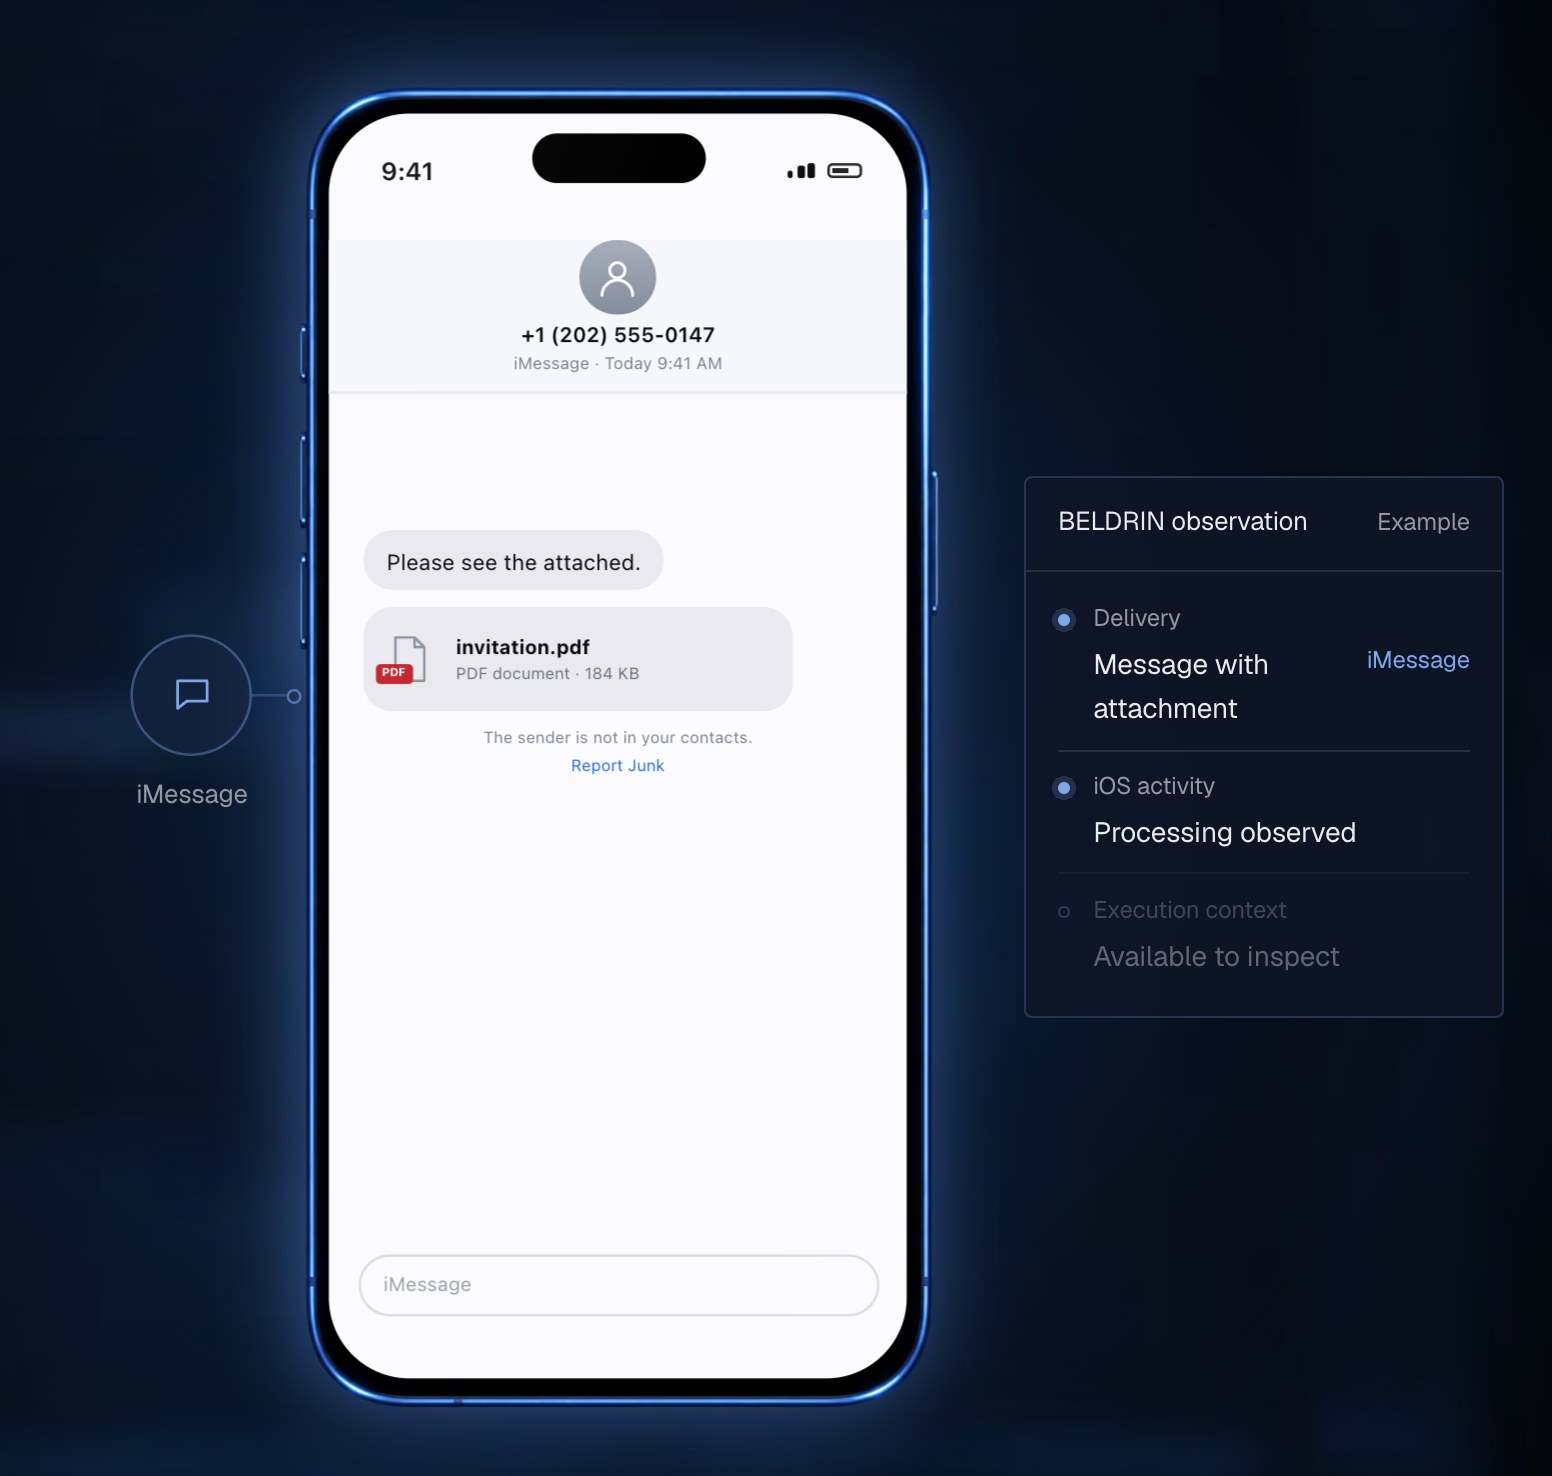
A message. A nearby transfer. An incoming call. Follow each one past the familiar interface, into BELDRIN’s capture and research environment.
iMessage. A message and its attachment reach iOS. Follow delivery and processing inside the research phone.
AirDrop. Nearby transfer activity reaches the research phone. BELDRIN connects the incoming event to the processing behind it.
FaceTime. A call request reaches the research phone. Observe the incoming activity and examine the execution context available for research.
Illustrative delivery paths and captured events.
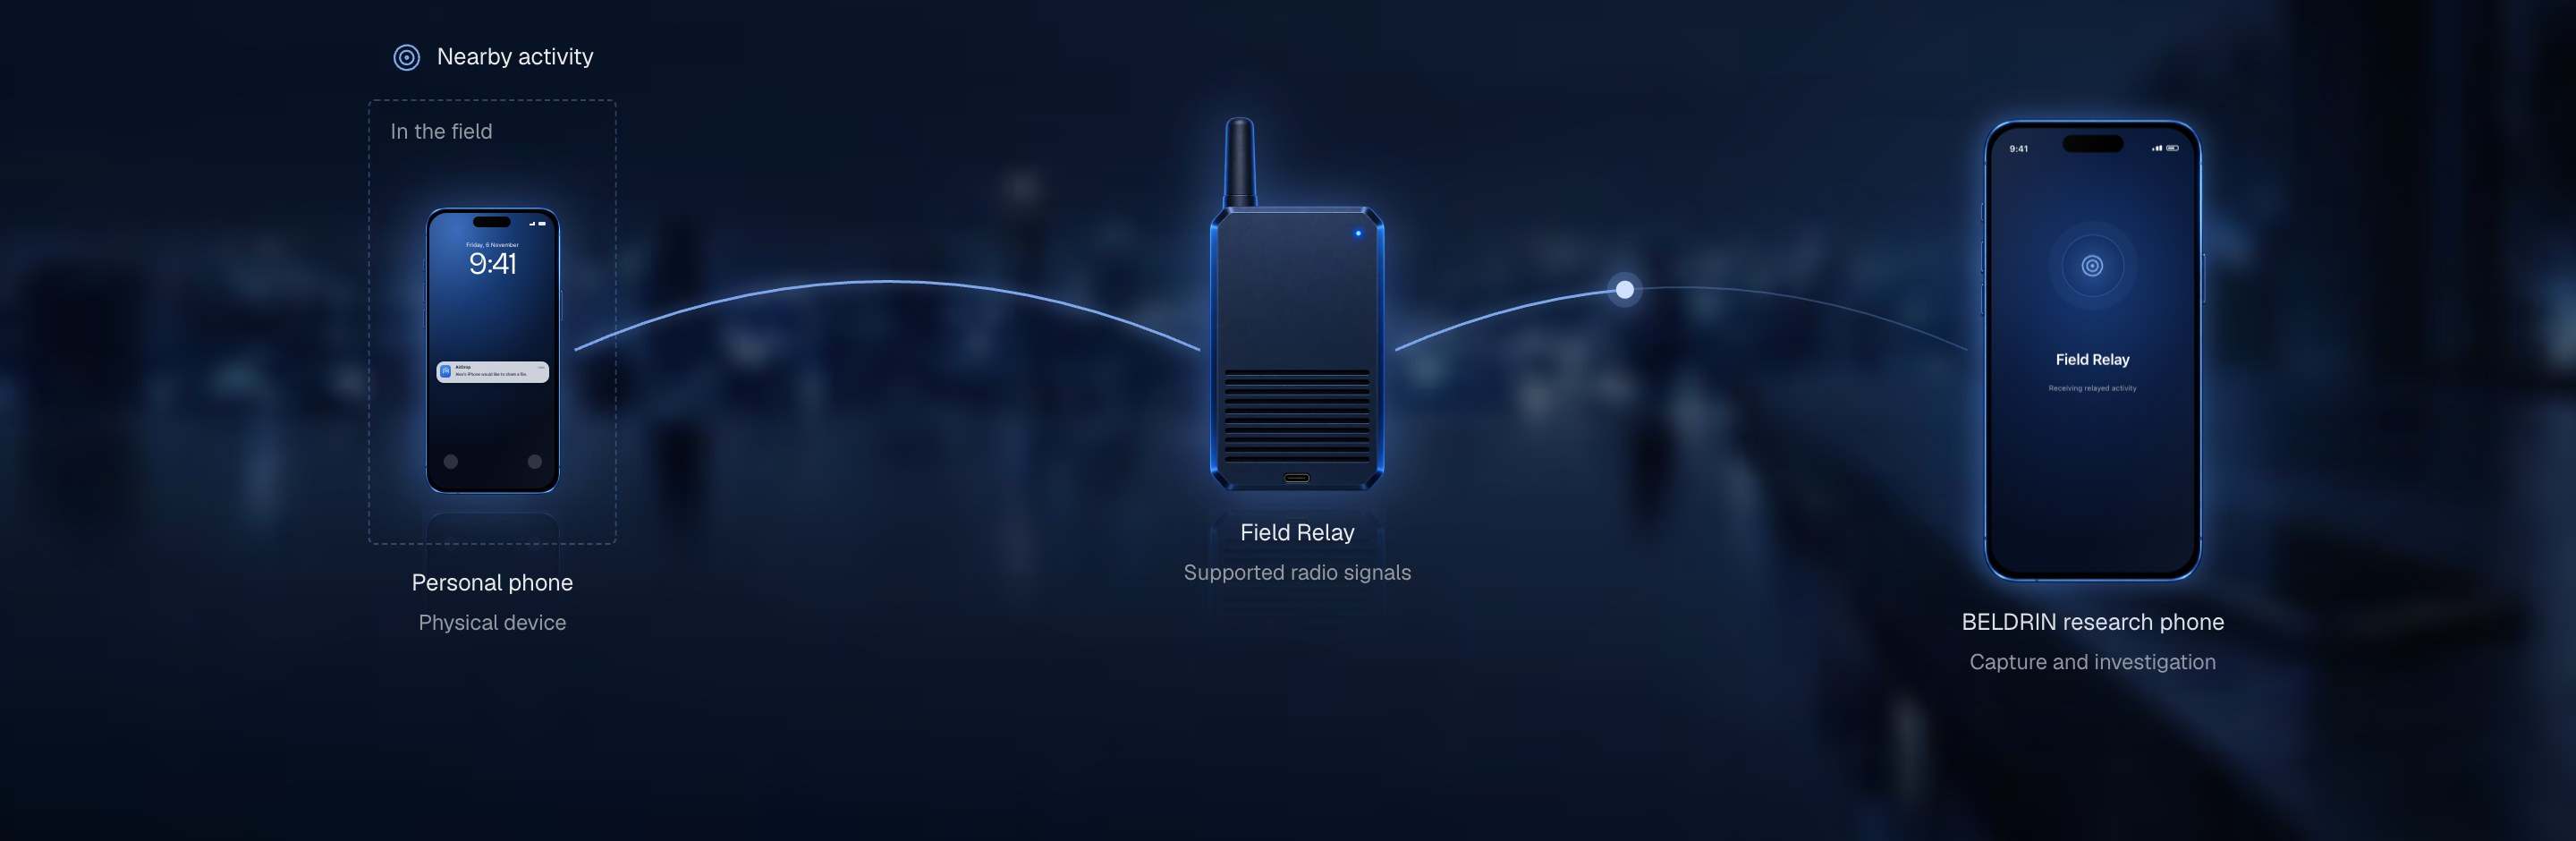
Field Relay accompanies senior officials, diplomats and executives, collecting supported radio signals around them and forwarding that activity to the BELDRIN research phone in real time.
Captured payloads and execution traces support investigations into targeted espionage, including suspected state-sponsored attacks. Security teams can examine the delivery, preserve the evidence and prepare a response.
Two devices. One investigation.
Activity around the individual
Field Relay collects supported signals
Relayed to BELDRIN for investigation
Supported radio connections only.
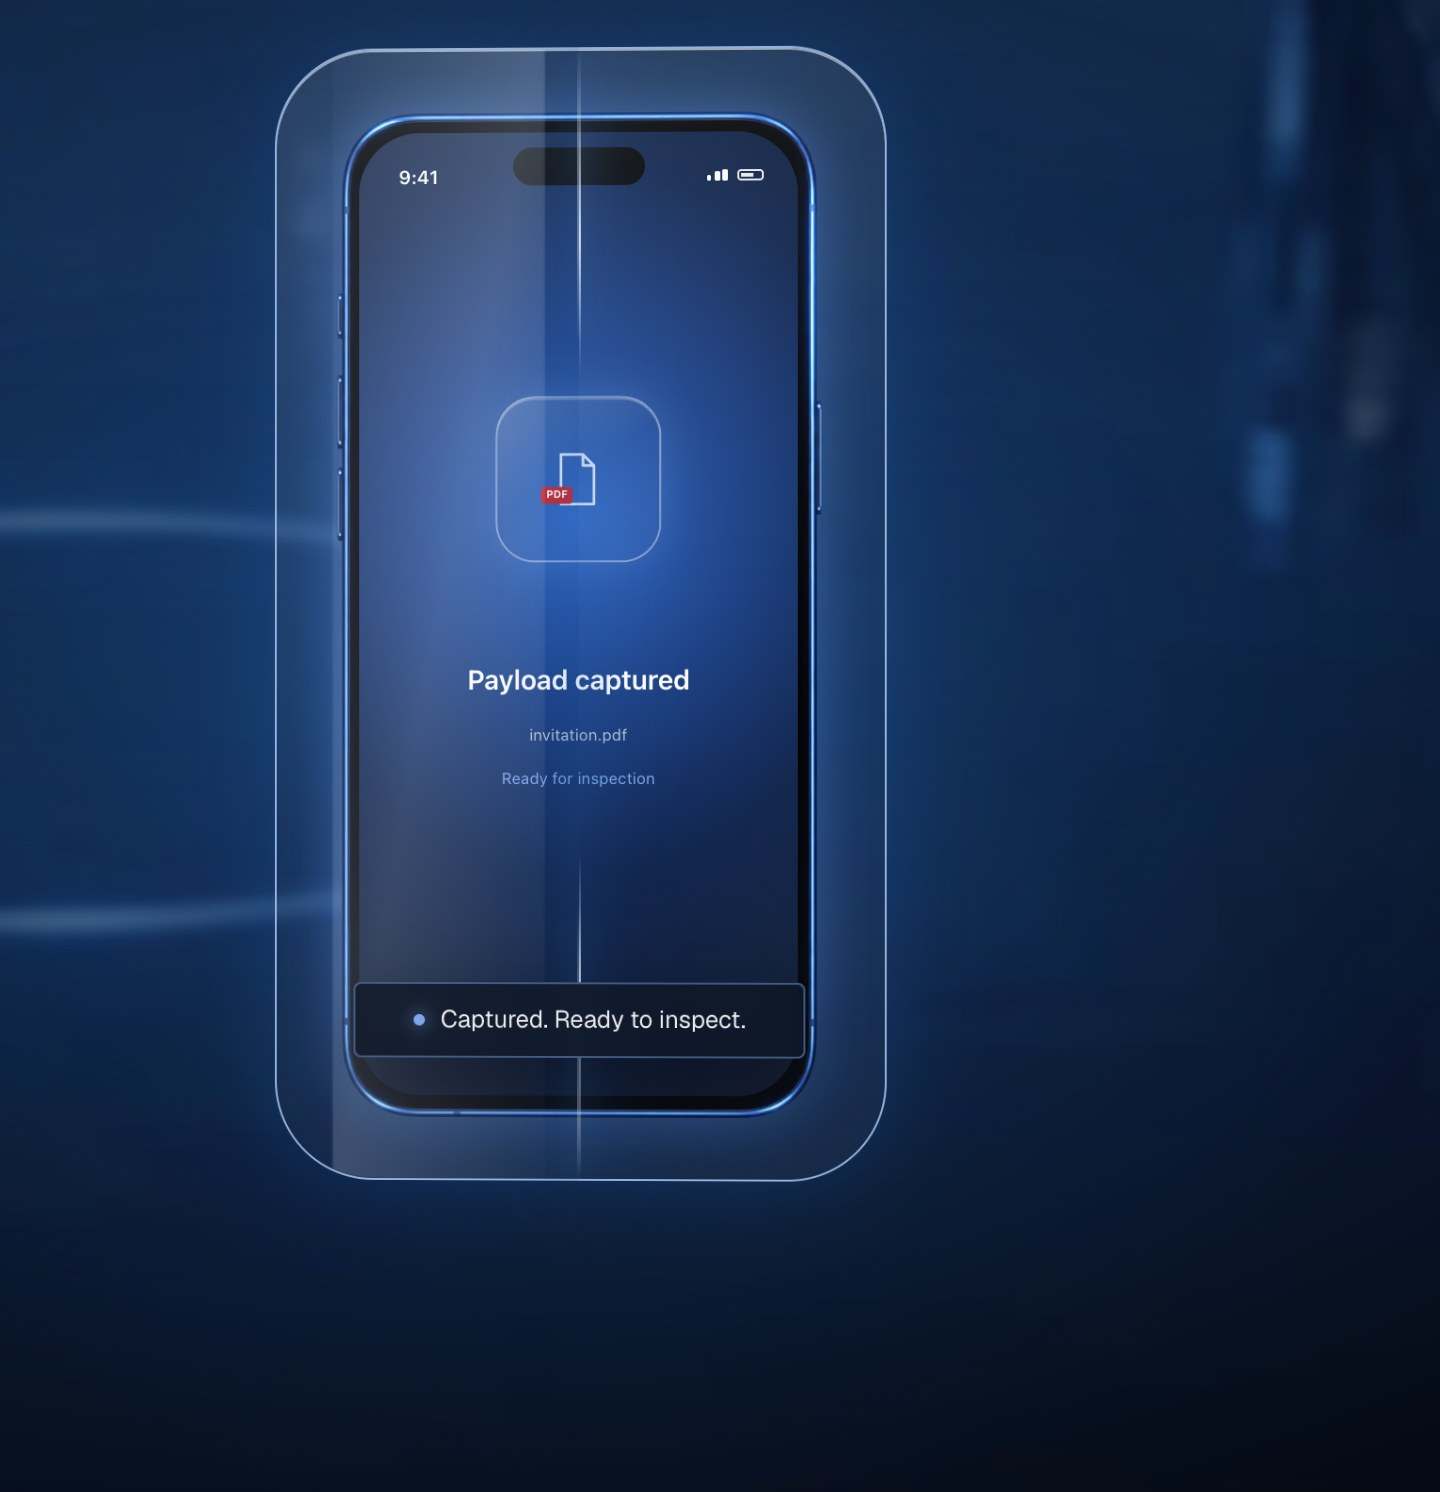
From cyber weapon to evidence.
Move from a suspicious delivery to the payload and its behavior. Examine the captured activity in BELDRIN and follow the execution behind the attack.
Incoming payloadResearch session
Illustrative scenario. No recorded attack data.
Follow a captured event into its execution context. Inspect kernel instructions, thread state and register changes, with the delivery context kept alongside the trace.
Representative trace. Synthetic addresses and instructions.
Instruction timeline
Disassemblymach_msg_trap_send
Read header. Read the preserved message size.
Registers
Call stack
Investigation use casesResearch and assessment of observed activity.
Exploit and payload research
Study the exploits and payloads used in targeted spyware, including threats such as Pegasus. Connect delivery to processing and execution.
Counter-espionage
Investigate suspected espionage against senior officials, diplomats and executives, including possible state-sponsored targeting. Connect delivery, captured payloads and execution context to establish what happened and inform the response.
Reverse engineering
Move from a captured payload to its execution context, then inspect the code path and kernel activity behind the attack.
Illustrative research workflows and analyst assessment.
One device. Every perspective.
Investigate the cyber weapons behind targeted espionage, from their delivery in the field to execution inside the device.
Capture
A connected research environment for examining payloads aimed at real people.
Connect
Bluetooth, physical SIM, eSIM, baseband and working Apple services.
Bring it in
Bring supported radio activity from the person’s surroundings into a controlled investigation.
Inspect
A debugger-like environment for examining where captured activity executed.
Take a closer look
Discuss your counter-espionage requirements, and we’ll take you through BELDRIN.
Contact